High False-Positive Volumes and Fragmented Evidence Slow AML Investigations
AML investigators often assemble transaction history, KYC data, watchlists, adverse information, prior case notes and relationship context across multiple systems. Rule-heavy alerting can generate significant false positives, while inconsistent data structures and manual “stare-and-compare” activity consume investigator capacity and slow escalation decisions.
Common challenges include:
- Fragmented investigation context: Transaction activity, customer information, watchlists and prior case history may sit across different systems and sources.
- Manual screening and research: Analysts can spend substantial effort gathering customer and transaction data before an alert can be assessed.
- High alert noise: Large alert volumes make it harder to focus investigative capacity on higher-risk or more complex cases.
- Inconsistent case summaries: Investigation findings can vary in structure and completeness when analysts must manually compile evidence and rationale.
- Compliance workload: Batch Escalation, SAR preparation and reporting require a clear audit trail from alert intake through investigator decision.
Context-Enriched AML Investigation with Screening, Analytics and Human Decision Control
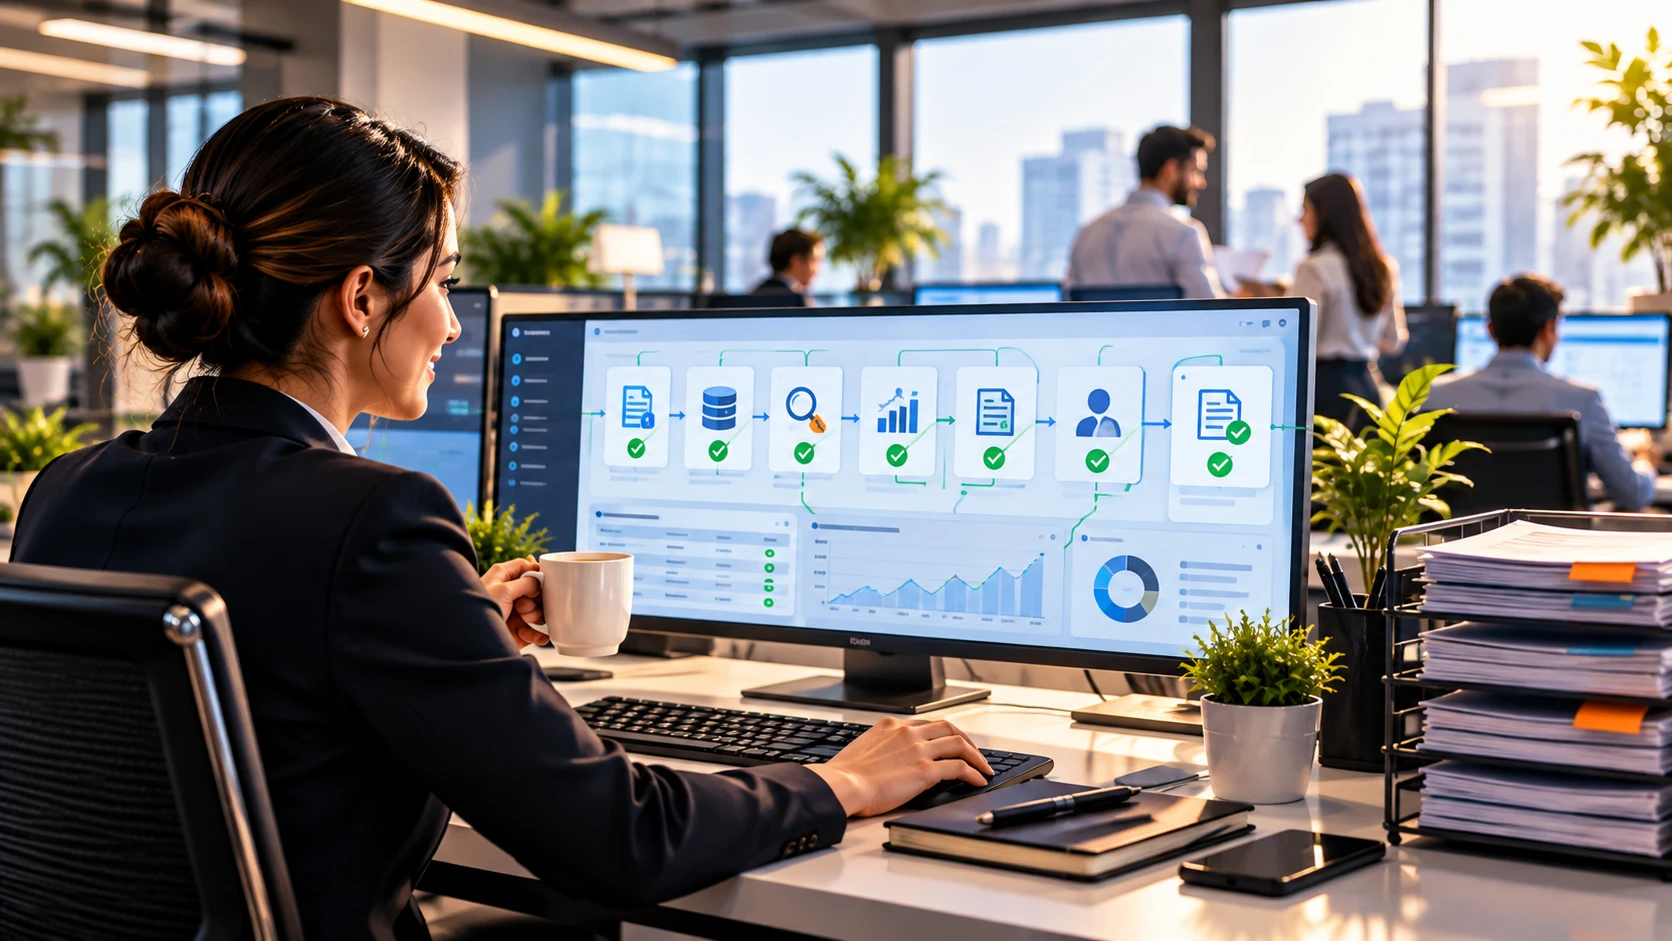
The workflow federates customer and transaction data, performs sanctions and PEP screening, applies behavioral and anomaly analytics, builds a concise investigation brief and routes the complete evidence set to the investigator. Final case disposition, SAR decisions and regulatory escalation remain human-controlled and fully traceable.
The solution uses:
- Automated alert and case intake: Create a consistent starting point for AML or financial-crime investigation workflows.
- Customer and transaction data gathering: Pull the account, customer and transactional context needed for investigation.
- Sanctions and PEP screening: Apply screening against relevant watchlists and defined compliance checks.
- Pattern and anomaly detection: Highlight suspicious behavior, unusual relationships or activity requiring deeper review.
- AI-generated investigation summary: Organize key findings, evidence and risk context into a concise analyst-ready brief.
- Human investigator review: Keep case disposition and escalation decisions with the compliance investigator.
- SAR / escalation support: Route confirmed concerns into the appropriate case-management and reporting process.
Quantified Evidence for More Efficient AML Investigation
<50%false-positive alert rate
Leading AML programs reduced false-positive alerts from above 90% to below 50% through analytics and better data aggregation.
<5% compliance-error rate
Sample-tested compliance error rates have been reduced from above 30% to below 5% in technology-enabled AML programs.
3× SAR conversion improvement
Tighter segmentation and analytics have produced threefold improvement in suspicious-activity-report conversion rates.
